AI agents are already raising orders, changing records and moving money inside your systems, on keys nobody can trace to a person. Sigilant makes every agent act as itself, with permission, with proof.
Three questions you will be asked about your agents.
Each one has an honest answer today, and it is not a good one. Sigilant exists so the answer becomes a record you can show.
The purchase order (from our demo)
"An agent raised a $48,000 purchase order on Friday night. Who approved it?"
Today: the agent used a shared password. The finance system logged the password, not the agent. Ten agents use the same one, so nobody can say which agent did it, for whom, or whether anyone said yes.
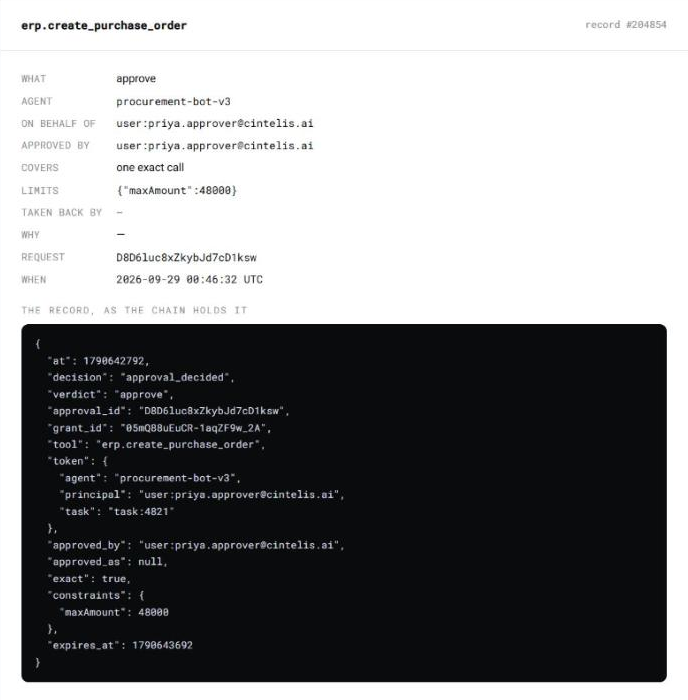
With Sigilant: the order was over the limit, so it waited. A named manager approved that exact order, and the record shows her approval.
The audit
"Show me your register of AI agents, and who owns each one."
Today: a spreadsheet, maybe. Government security rules now expect a list of every AI agent and who is responsible for it, and regulators expect you to stand behind the work they do.
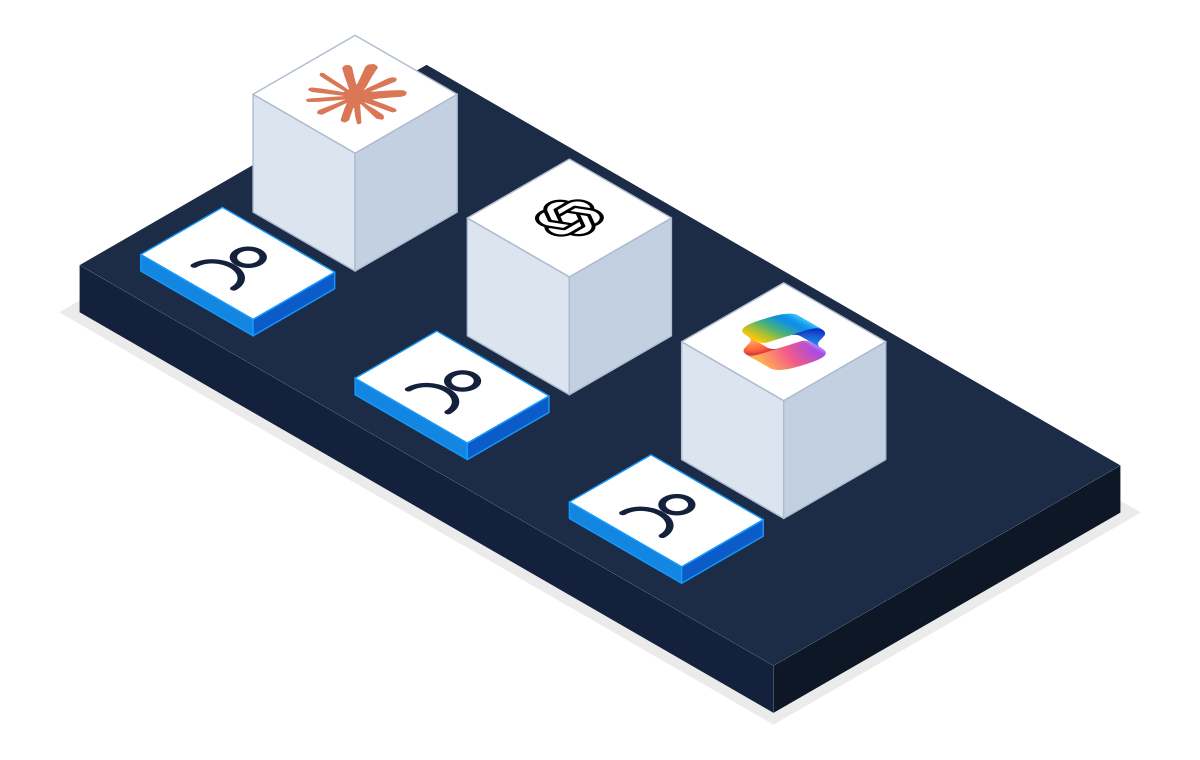
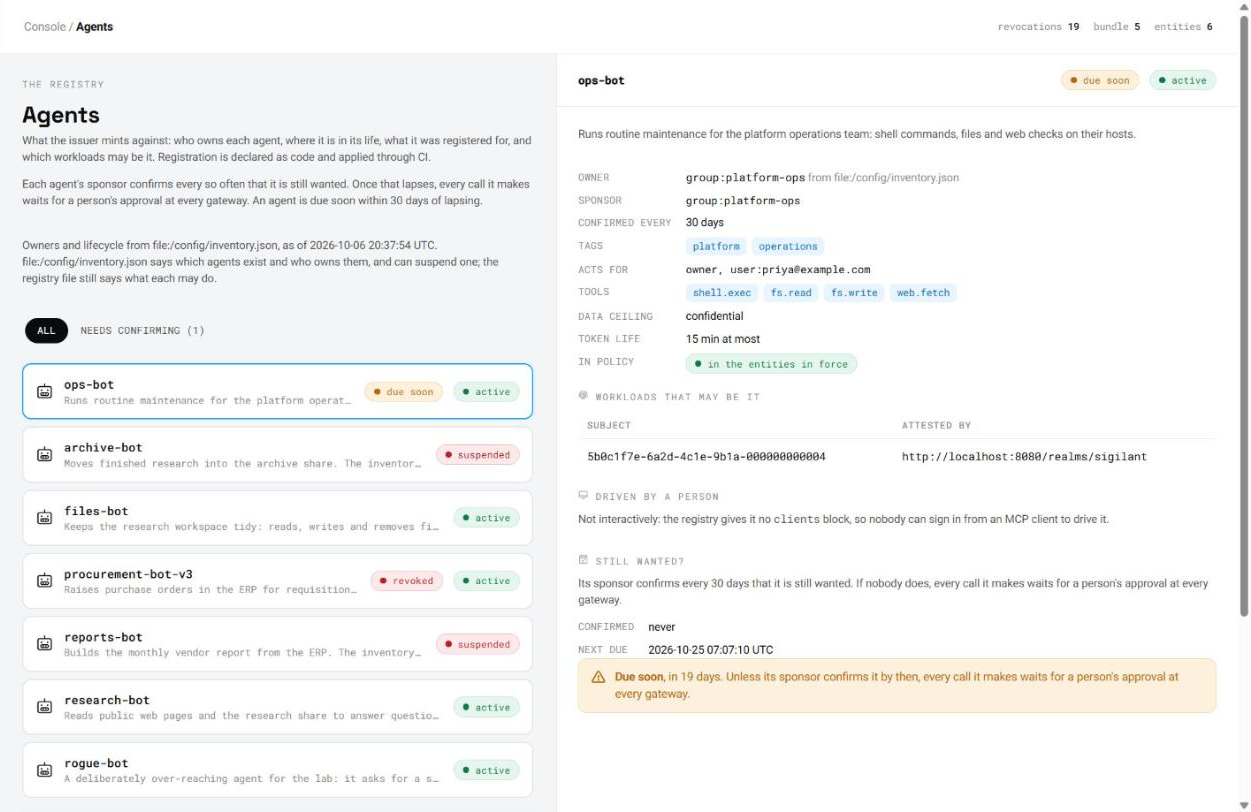
With Sigilant: every agent is on the list with a named owner, who confirms every so often that it is still needed. An agent nobody vouches for stops and waits for a person.
The rollout
"Security said no. The agent would need the finance system's password."
Today: the safe answer is no, so the project stalls. Or it goes ahead with a password hidden inside the agent, and everyone hopes.
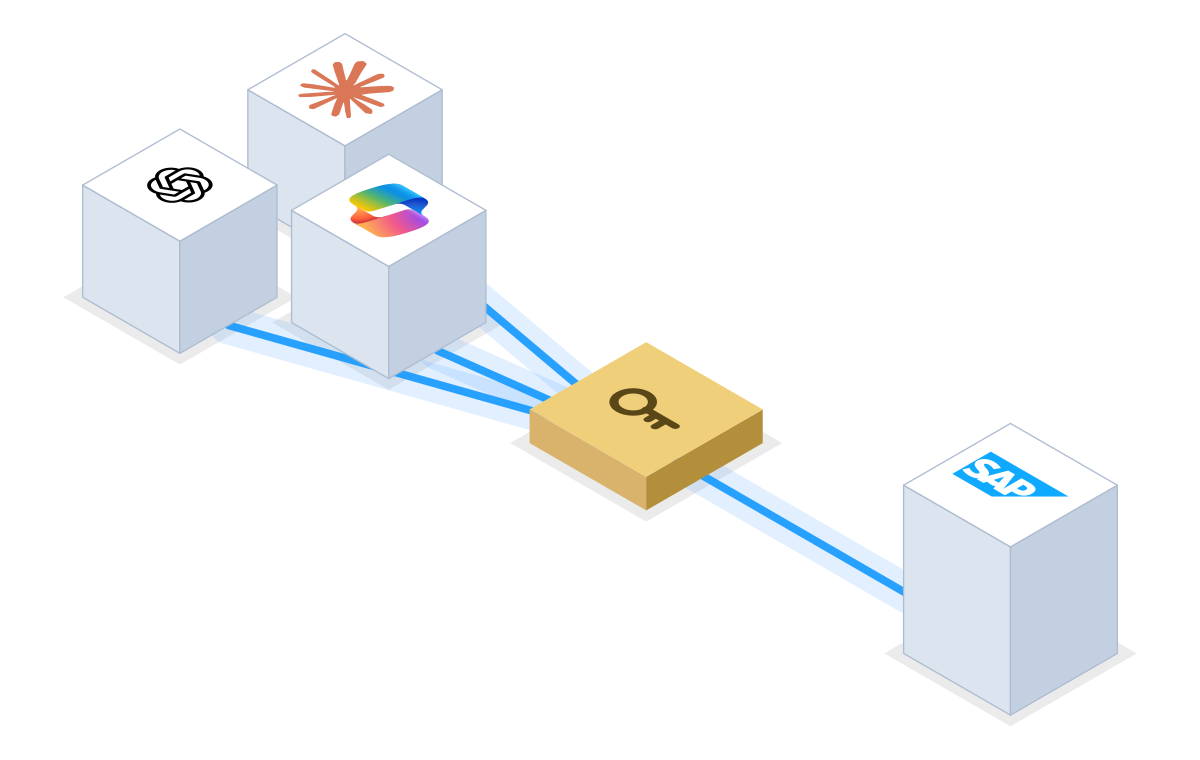
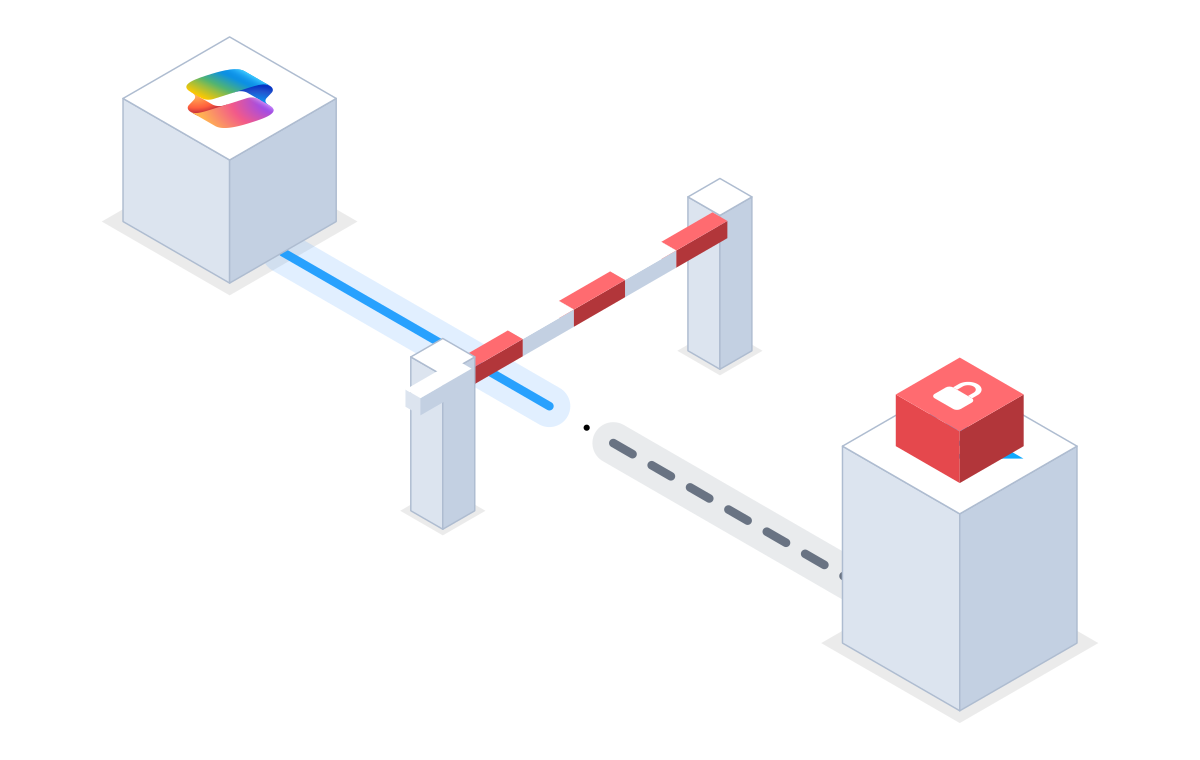
With Sigilant: the agent never holds a password. Sigilant lets it in for the one approved action, then closes the door. Security can say yes.
What it costs you today
Four things that are true until an agent has an identity.
01
You cannot answer the regulator
Who did it, on whose behalf, and who approved it. Three questions, no reliable answer.
02
You cannot stop it in time
Turning off a shared password breaks everything that uses it. So nobody does, until it is too late.
03
You do not know how many you have
Agents arrive inside software you buy and tools your teams build. The ones you cannot see are the ones that hurt.
04
You are the one saying no
Every agent the business wants is a risk you carry personally. Saying yes needs something to point to.
A real run
What governing one agent looks like, minute by minute.
From our demo: a purchasing agent, a manager called Priya, and a finance system. Nothing in the agent or the system was rebuilt.
1Priya logs in the way she always does. Her agent is now known as hers.
2Her agent raises a purchase order for $48,000.
3That is over the company's limit, so Sigilant holds it. The finance system has not seen it.
4Priya sees exactly what is waiting and approves that order, and only that order.
5Only now does the finance system accept the order.
6Later, someone switches the agent off. It stops at once, along with everything it started.
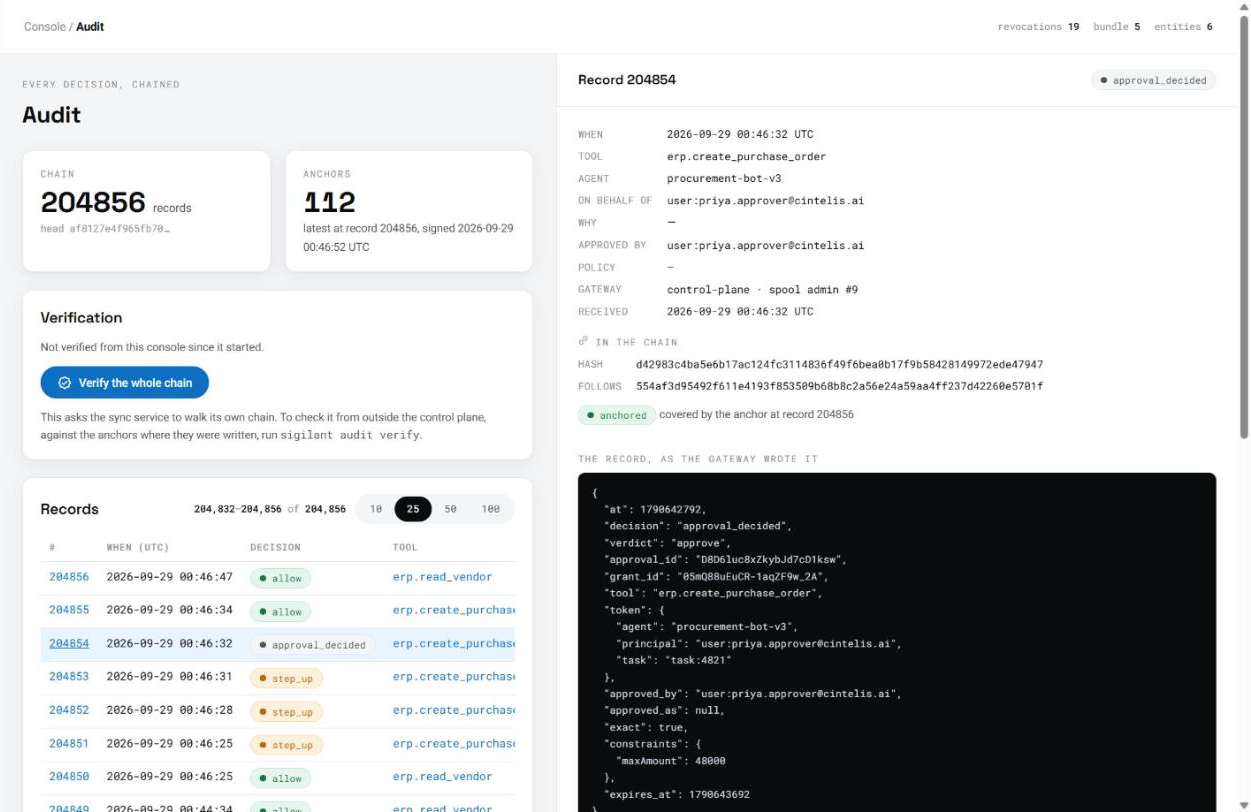
The approval, as the record holds it: which agent, for whom, approved by whom, for this call only.Every decision on one record that cannot be quietly changed. Your auditor can check it without taking our word for it.The list of agents: who owns each one, what it may touch, and when its owner last confirmed it is still needed.
How it works
One checkpoint. Four things happen at it.
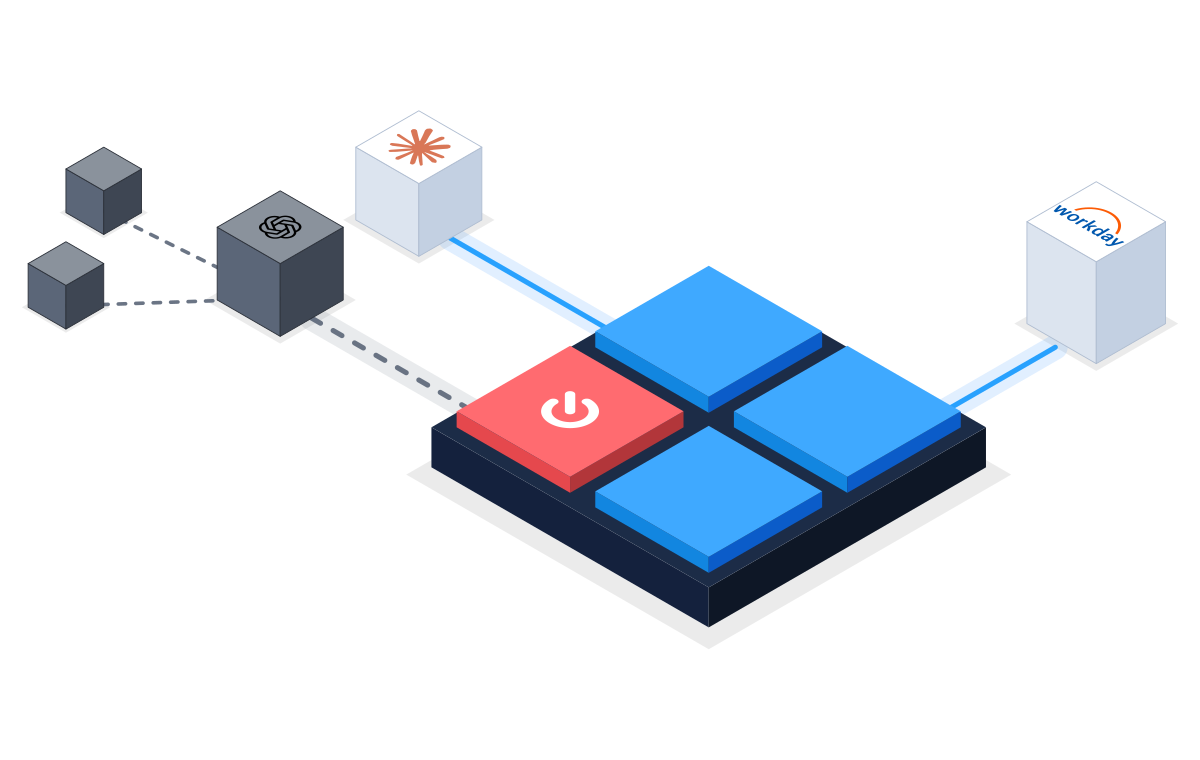
Agents go through Sigilant to reach your systems, instead of going straight in. Neither the agent nor the system behind it has to be rebuilt.
Step 01
Decide
Each action is checked against your rules before it happens: which agent, for whom, doing what.
Allow, hold or refuse
Step 02
Approve
Actions you mark as high-risk are held for a named person, who sees exactly what they are approving.
A person in the loop
Step 03
Access
The agent never holds the keys to your systems. Access is supplied for the one action, then gone.
Nothing to steal
Step 04
Record
Every decision, allowed or refused, is written to a record that shows if it has been altered.
Evidence as a by-product
What you can now say
Six sentences for the board.
Each one is a capability, written the way you will have to say it.
Every agent has a named owner, who confirms every so often that it is still needed.
Nothing happens outside our rules. Each action is checked as it happens, not once when access was first given.
Big actions were approved by a named person, and the approval covered that action only.
No agent holds a password to our systems. It is let in for one action, then the door closes.
We can stop any agent, and everything it started, at once. Even halfway through a task.
Our records can be checked by anyone, without trusting us or our supplier, and they are protected against tomorrow's code-breaking computers.
The kill switchThe record
Find them first
Find the agents you did not know you had.
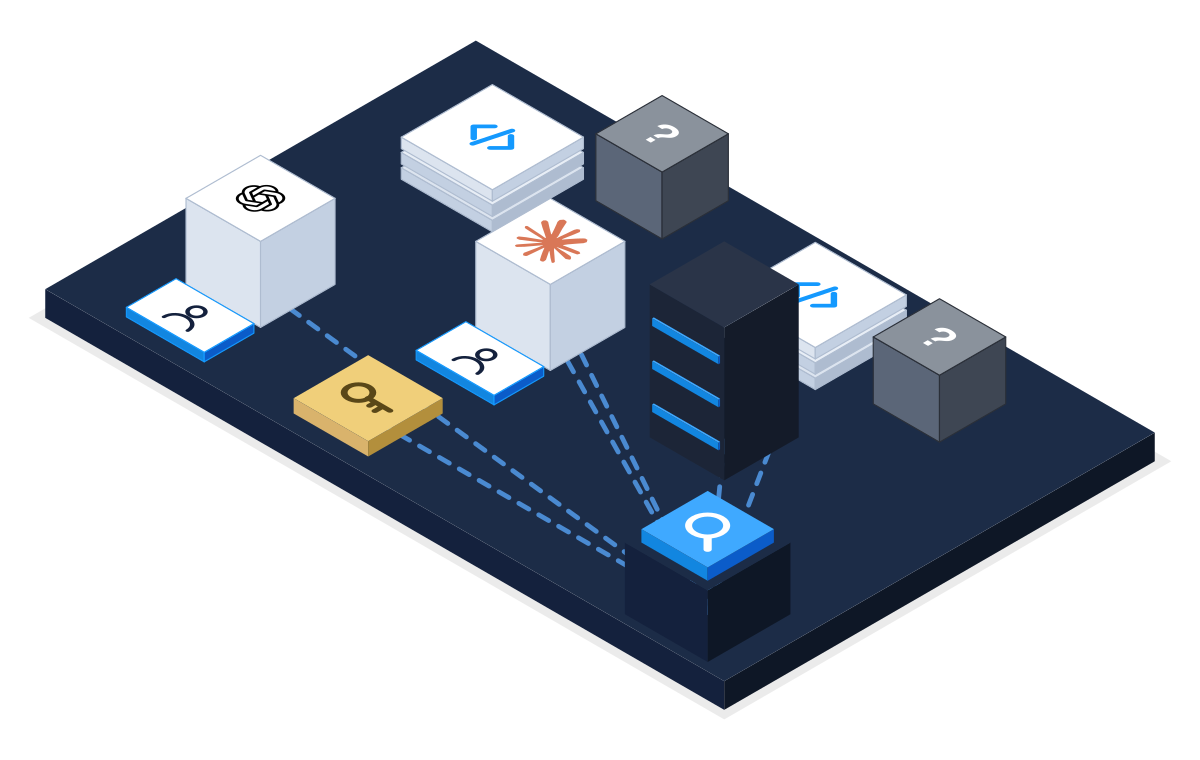
AI agents arrive inside software you buy and tools your teams build, and most organisations only meet theirs during an incident. Sigilant looks first: it searches your code and your systems for AI agents, AI tools and passwords to AI services, and asks a person to claim each one or switch it off.
It keeps looking. Every change your teams make, every release and every day, it checks again, so "are we still safe?" has an answer you can show, not a feeling.
Deployment
Built to fit what you already run.
Your people log in and approve with the login system you already use, such as Okta, Auth0 or Microsoft Entra ID, and agents belong to the teams you already have. Sigilant runs on your own systems: your rules, your records and what your agents do stay with you.
IdentityWorks with your existing logins
AgentsWorks with the AI agents you already use
HostingRuns in your environment
FailureIf it cannot decide, it refuses
CryptographyProtected against future code-breaking
EvidenceRecords nobody can quietly change
Bring one agent and one system it touches.
We will show you how Sigilant controls it, on your systems, with your rules. One hour, and you leave with the record.